Modern Application Framework: Structure…
Breaking into product management can feel confusing when job descriptions…
An invoice workflow can fail because of a weak integration, even when AI reads every document correctly. Checking the supporting systems before expanding automation helps reveal problems that a model accuracy score cannot show.
For enterprise teams, a Best Practice Analyser compares a supported system or data model with a defined set of technical rules. It identifies deviations for review, with coverage determined by the product, permissions and available information.
Those findings can guide improvements across enterprise business and technical solutions when combined with process reviews and custom tests. AI assistance can help explain and organise the work, while people remain accountable for consequential decisions.
The first question is whether the analyser supports the system you need to assess. Product names alone do not establish coverage.
Microsoft’s Best Practices Analyzer checks supported Windows Server roles against technical recommendations. Tabular Editor’s Best Practice Analyzer examines metadata in Power BI and Analysis Services models. Their findings address different parts of a technology environment.
A wider enterprise review may also need checks for customer relationship management (CRM) permissions, application programming interfaces (APIs), deployment settings and AI behaviour. An API is the interface through which software systems exchange requests and data.
A clean report means the completed checks found no violations of their rules. Untested areas still need attention.
A technical warning needs context before it becomes a priority. The affected process, likely consequence and available recovery options matter alongside the tool’s severity label.
Consider a customer record that passes from a CRM into an order-processing application. A permissions issue could interrupt that handover or expose information to an unintended account. Reviewing the finding means understanding both the setting and the business dependency.
A useful assessment record includes:
This gives decision-makers something more useful than an unexplained list of warnings.
AI can help teams understand findings and prepare follow-up work. These functions require a suitable integration; they are not built into every rule-checking tool.
For example, an assistant could group related findings, explain technical terminology and draft an investigation ticket. It should retain the original evidence so a reviewer can distinguish the observed issue from the suggested explanation.
Generated text can contain convincing errors, including incorrect assumptions about settings or dependencies. Reviewers should check recommendations against approved documentation and the actual environment before accepting them.
Ordinary workflow rules may be enough to assign tickets or send reminders. AI earns its place where interpretation is useful and its output can be checked without creating excessive review work.
A sound review ends with a checked outcome. The steps below provide a practical starting point for a defined business process.
Keep a record of accepted exceptions and unresolved coverage gaps. A skipped check is missing evidence, and a corrected setting still needs confirmation in the working process.
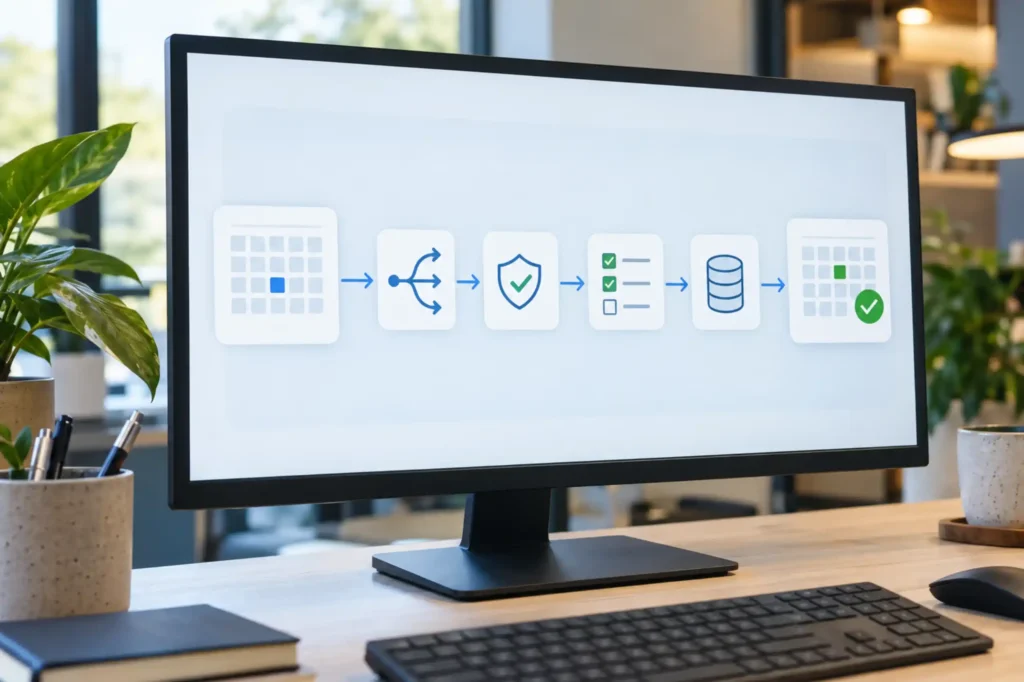
Suppose a company uses AI to extract invoice details, custom software to validate them and an API to create accounting records. This is an illustrative scenario, not a claim about a completed project.
A review could combine infrastructure checks with custom tests for missing supplier identifiers, repeated submissions and service-account access. A separate evaluation would compare extracted fields with representative invoices.
If a connection retries after a timeout, the application should prevent the same invoice from creating duplicate records. Uncertain extracted values should enter a review queue rather than move forward unchecked.
An AI assistant could summarise failures and prepare investigation notes. The team would then verify approved changes against processing errors, invoice accuracy and review workload.
Start with a process whose systems, owners and expected behaviour are understood. Completing that review provides a clearer basis for expanding coverage than collecting more warnings without resolving them.
Success means making a justified change and showing what happened afterwards. AI assistance should improve the quality or efficiency of that work, with its errors included in the assessment.
For a practical starting point, consider discussing one enterprise workflow and its assessment requirements with Ebtechsol.
Not inherently. Many analysers apply predefined rules without AI. An organisation can add AI to interpret results or draft follow-up work, but that requires separate design and evaluation.
Only within its supported scope. Assessing a complete workflow usually means combining tool results with integration tests, process knowledge and a record of dependencies that individual scanners cannot see.
No. A passed check confirms a particular rule was satisfied under the conditions tested. Security also depends on factors beyond that rule, including application behaviour, access controls and changing threats.
Identify the systems, versions, owners and expected business outcomes. Confirm access requirements and applicable rules, then agree what falls outside scope so missing coverage is visible from the start.
Limit access to authorised people and services. Before sharing findings with an AI provider, remove unnecessary sensitive details and review how the service handles retention, access and processing.
No. Investigate whether the warning applies to the environment and whether the proposed fix creates other problems. Document justified exceptions with an accountable owner, rationale and review date.
Review them when systems, dependencies or business requirements change, as well as on a risk-based schedule. Reusing an old rule set without checking its relevance can leave important gaps.
That depends on the tool and available rules. Custom integrations often need dedicated tests for request validation, permissions, failure handling and retries, alongside checks of the infrastructure supporting them.
The people responsible for the affected service and change risk should approve consequential actions. An AI-generated recommendation does not transfer accountability or remove the need to test its assumptions.
Compare outcomes with the baseline: recurring failures, investigation time, review effort and unresolved risks. Include the cost of maintaining checks and correcting poor recommendations when judging the overall value.
Breaking into product management can feel confusing when job descriptions…
Breaking into product management can feel confusing when job descriptions…
Breaking into product management can feel confusing when job descriptions…

EB Technical Solutions FZE /
EB TECHNICAL SOLUTIONS (PVT.) LIMITED
Copyright © 2026 EBTECHSOL

Ask me anything about AI Automation, API Integration, SaaS Development or our Services.
Just get in touch via text or microphone.